Connect With Us
Whether you want to discuss CI-Discern's Sectors, Services, or have a conversation about your environment, click “Contact us” to speak with a leading expert.
Advisory, architecture, governance, and assessment services for critical infrastructure.
All services CISO Advisory & AmplificationExecutive security leadership, extended.
 IT/OT Strategy, Architecture & DesignArchitecture that protects the process.
 C-Suite, Board & Government AdvisoryDecision-ready insight for leaders.
 Security Governance, Risk & ComplianceAccountability that holds up to scrutiny.
 Assessments & Audit ReadinessKnow where you stand. Prove it.
CCE
CCE Risk AssessmentConsequence-driven assessment, approved DOE/INL licensee.
CMMC
CMMC Advisory & AssessmentGap, advisory, and readiness assessment for defense suppliers.
Advisory, architecture, governance, and assessment services for critical infrastructure.
Every engagement starts with what you cannot afford to lose. Our practitioners have held the security and technology leadership roles our clients hold today, and they work alongside your team to set strategy, secure IT and OT environments, meet regulatory obligations, and prepare leadership to act with confidence. Use one service on its own or combine them into a single program.
Former CISOs work alongside your team to set strategy, strengthen your program, and tie cybersecurity to the outcomes your leadership and operations depend on. Engage us as an interim or virtual CISO, or as an advisor to the one you have.
Security strategies and architectures built to protect critical environments, reduce real-world risk, and keep operations running.
We give executives, boards, and government leaders a clear view of cyber risk, so they can set priorities with confidence, strengthen oversight, and lead decisively when it matters most.
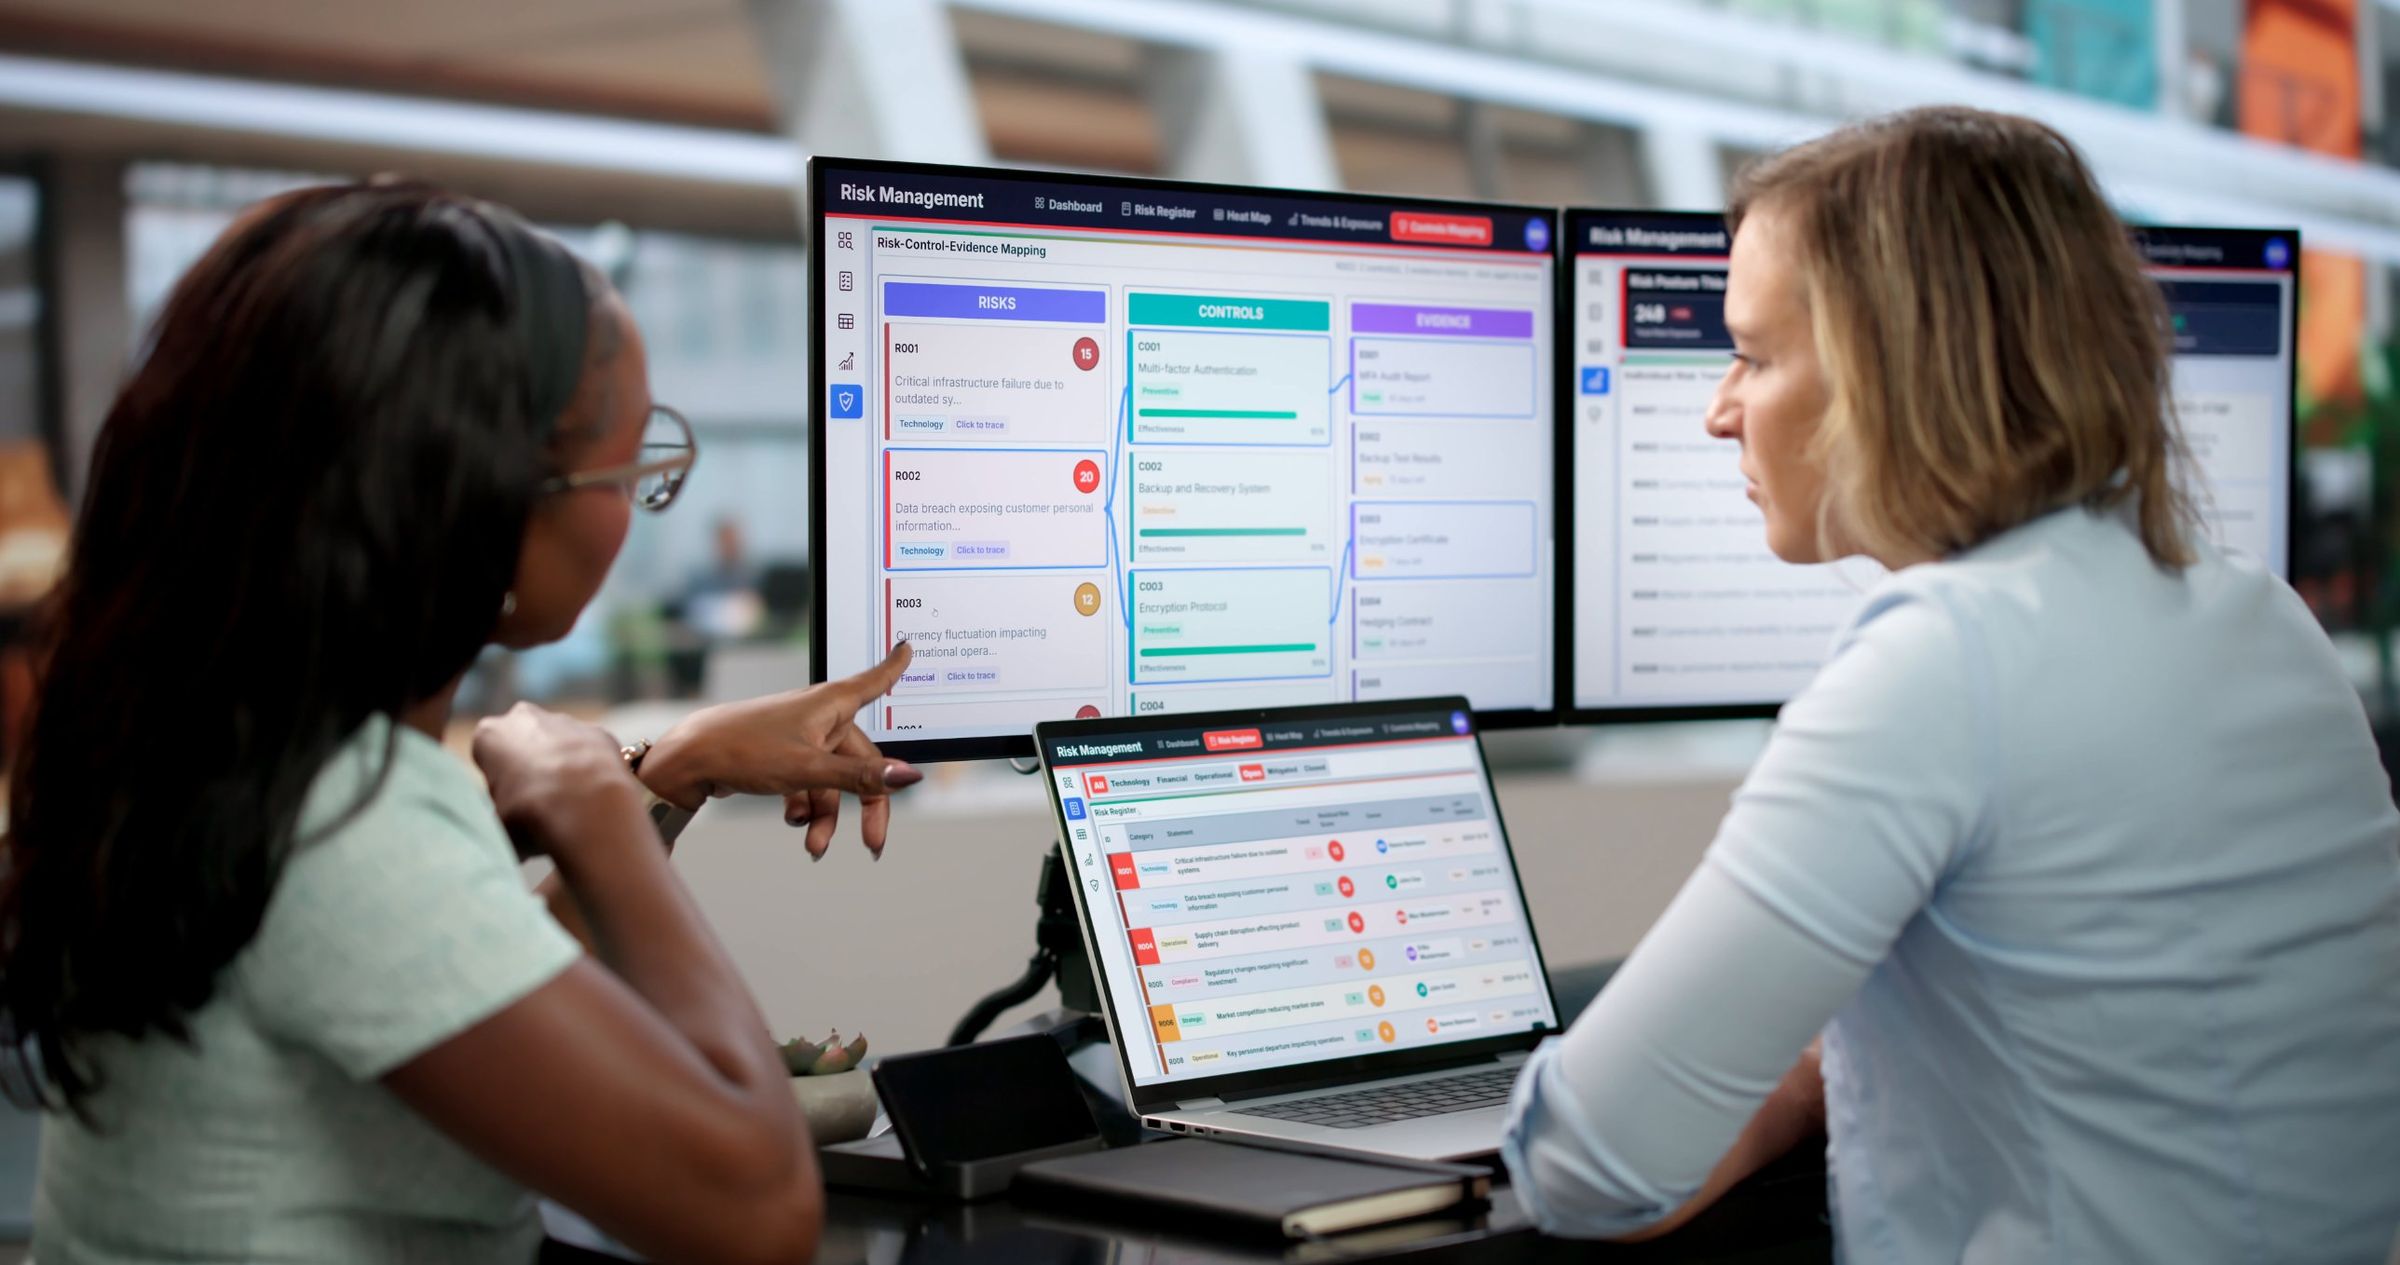
We build practical governance, risk, and compliance programs that clarify ownership, align controls across frameworks and regulators, and turn compliance into lasting resilience.
We assess your environment against recognized standards and industry best practices, showing what is working, where to improve, and which steps will strengthen your security and readiness most.
CI-Discern applies Consequence-driven Cyber-informed Engineering (CCE), the methodology developed by Idaho National Laboratory, to identify the outcomes your organization cannot accept, map how an adversary could cause them, and engineer protections that remove or reduce those consequences.
Certified CMMC Professionals and Certified CMMC Assessors on staff help defense suppliers find their gaps, close them, and prepare for certification. We are not a C3PAO, so our guidance stays independent of the certification decision.
Whether you want to discuss CI-Discern's Sectors, Services, or have a conversation about your environment, click “Contact us” to speak with a leading expert.